Guides
Getting the databook table of contents approved at kickoff
A line that shows up in plenty of book specifications: submit the databook structure and table of contents for approval…
Read Now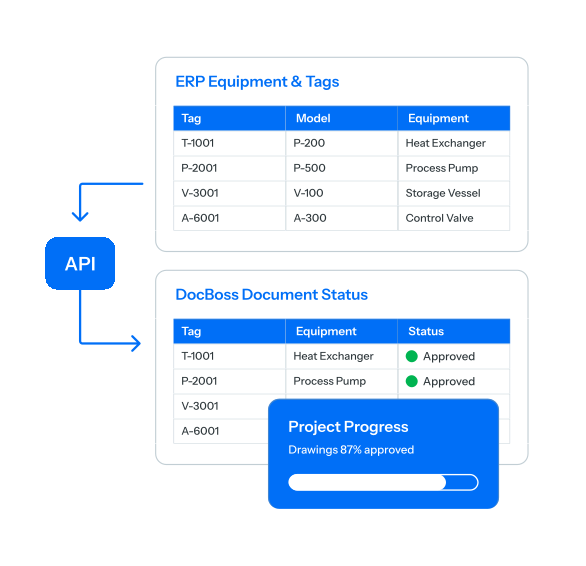
Move equipment, model, and tag data directly from your ERP into DocBoss, or pull live completion metrics back into your ERP dashboards.
Align user authentication with enterprise standards, restrict permissions down to specific roles, and maintain clear security boundaries across every division.
Identity
Users are managed where you already manage them. Joiners and leavers follow your existing process rather than depending on a document control administrator remembering.
Divisions
Separate business units, joint ventures and regional operations run as separate affiliates on one system, with their own outputs and their own user access.
Precision
Four role types plus per-user permissions, so an engineer who reviews drawings cannot reconfigure a project.
Integration
Projects created from your order system, equipment lists and document codes loaded from your ERP, library files kept in step. Data is entered where it already lives.
Answers
Security questionnaires are answered directly by people who know the system rather than deflected to a trust page.
Schedule a 15-minute walkthrough to see how DocBoss plugs directly into your existing ecosystem.
Manage multi-affiliate setups, automate data flow via open APIs, and onboard teams through SCIM user provisioning without disruption.
Authenticate users through your identity provider using SAML 2.0 with SCIM 2.0 provisioning for Microsoft Entra ID, Okta, or Ping. Account creation, updates, and deactivation automatically follow your standard identity lifecycle.
Mark sensitive projects as confidential to restrict visibility strictly to explicitly granted users. Confidential status flags directly in the project list so data protection is clearly indicated rather than assumed.
Automate project creation from your order system, load equipment lists from ERPs, and sync library files via documented API endpoints. API access is included as part of the core product without separate licensing fees.
DocBoss support cannot enter your system unless access is deliberately granted. Support permissions expire automatically and can be instantly revoked by an administrator at any point.
Assign four primary role types—view, review, full, and admin—to match team responsibilities. Individual user permissions can be scoped to specific projects to ensure appropriate access boundaries.
Run separate divisions, joint ventures, or regional entities on one system with isolated document codes, templates, and email addresses. Users access only assigned affiliates, while standard manuals can be shared across divisions.
Enforce MFA instance-wide or target specific roles, including external portal contacts and sub-suppliers. Separately require submittal recipients to confirm their identity before downloading files.
Hosted on AWS with versioning enabled to prevent accidental file deletion. System volumes are snapshotted hourly, retained for two weeks, encrypted, and regularly tested for restore validity.
Get answers to questions about Access & Security
No. With provisioning enabled, users are created, updated and deactivated from your identity provider over SCIM, and they sign in with the credentials they already use.
SAML 2.0 for single sign-on and SCIM 2.0 for provisioning, with Microsoft Entra ID, Okta and Ping. Configuration is done with DocBoss support rather than left to you to work out.
Yes. Each division runs as its own affiliate with its own document codes, templates, project settings and outbound email, and users reach only the projects belonging to the affiliates they are assigned to. Shared reference documents can still be made available across all of them.
Get answers to questions about Access & Security
No. With provisioning enabled, users are created, updated and deactivated from your identity provider over SCIM, and they sign in with the credentials they already use.
SAML 2.0 for single sign-on and SCIM 2.0 for provisioning, with Microsoft Entra ID, Okta and Ping. Configuration is done with DocBoss support rather than left to you to work out.
Yes. Each division runs as its own affiliate with its own document codes, templates, project settings and outbound email, and users reach only the projects belonging to the affiliates they are assigned to. Shared reference documents can still be made available across all of them.
Learn how teams just like yours transformed complex customer formatting, cover sheet rules, and databook assembly into a push-button workflow.
A line that shows up in plenty of book specifications: submit the databook structure and table of contents for approval…
Read NowDocument requirements on equipment orders multiply. One test report per tag. One general arrangement drawing per model. One packing list…
Read Now